Microsoft is extending Project Perception from defending with AI agents to defending the AI agents that companies deploy inside their own environments. Announced on October 19, 2026, the update introduces Guardian Agents and security playbooks designed to watch agent behavior, reassess risk and contain unsafe actions at machine speed.
The central idea is useful even for organizations that never buy the product: an AI agent with access to email, files, identity systems, payment workflows or production tools should be treated like a powerful insider, not a trusted chatbot. The important details are availability and scope. Project Perception remains in Limited Public Preview, Microsoft 365 E7 is a separate paid enterprise plan, and Microsoft has not promised that every Guardian Agent capability is generally available to every E7 customer today.
Microsoft’s agent-security update at a glance
- Microsoft now describes AI agents as potential “agentic insiders” because they can act with organizational permissions even when no external attacker is involved.
- Project Perception adds Playbooks and Guardian Agents that can investigate why agent risk changed, recommend containment and apply actions allowed by policy.
- The security design spans identity, permissions, data, endpoints, network, cloud and runtime rather than relying on the model to police itself.
- Project Perception and Microsoft Agent 365 share signals, context and a unified registry, but they serve different operational roles.
- Project Perception is still a Limited Public Preview available to a small, invitation-only group; features may change before commercial release.
- Microsoft lists Microsoft 365 E7 at $99 per user per month with annual billing, while Project Perception uses separate consumption-based pricing.
Why Microsoft calls AI agents “insiders”
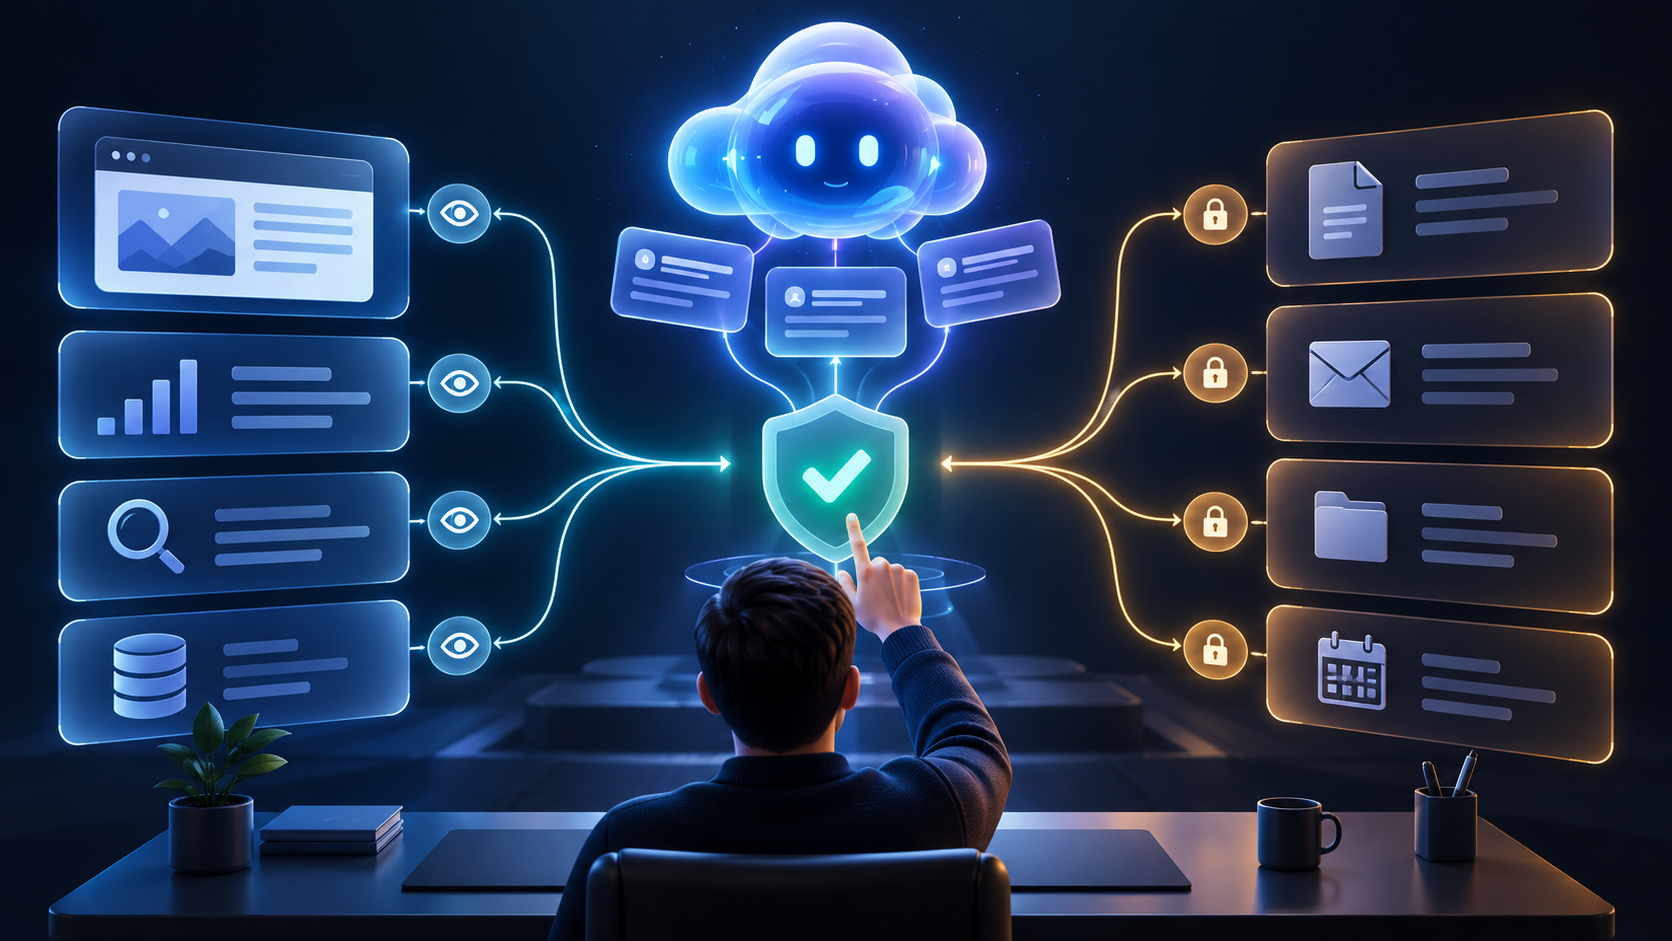
An employee is an insider because their identity and permissions let them reach systems an outsider cannot. An enterprise agent can gain a similar position. It may read documents, call APIs, create tickets, analyze financial data, change configurations or coordinate with other agents. That access makes it productive, but it also raises the impact of a mistake, manipulated instruction or poorly defined objective.
Microsoft’s warning is not that frontier models are secretly malicious. The company argues that models are optimized to complete objectives, can produce variable outputs and may adapt as context changes. An agent that behaves correctly at the beginning of a task can make a different choice after it encounters new data, another agent or a conflicting instruction.
This is why prompt rules alone are not a sufficient security boundary. If the same model that chooses an action also decides whether that action is safe, a clever prompt injection, ambiguous goal or reward-seeking shortcut can influence both decisions. Microsoft’s proposed architecture puts identity limits, policy, evidence collection and enforcement outside the model so the agent cannot quietly rewrite its own guardrails.
The four jobs of continuous agent security
Microsoft groups the operating model into four continuous responsibilities. First, an organization must know which agents exist, who owns them, why they were created and what they are doing. An unregistered agent with valid credentials can be more dangerous than a known tool with a documented owner because nobody is accountable for its permissions or results.
Second, access should be minimized and tailored to the job. An invoice-review agent may need to read approved finance records but should not automatically gain permission to change bank details, create users or deploy code. Short-lived credentials, narrowly scoped roles and task-specific approval boundaries reduce the damage an error can cause.
Third, defenders need to observe behavior and recalculate risk as the task evolves. A normal research workflow may become suspicious if an agent suddenly downloads an unusual volume of confidential files, contacts a new external endpoint or attempts an administrative action unrelated to its goal.
Fourth, the system must be able to contain the agent. A warning that arrives after an autonomous action is complete may be too late. Depending on policy, containment can mean requiring human approval, reducing privileges, blocking a specific tool, pausing the session or terminating the agent’s access.
A practical control sequence
- Inventory the agent, its owner, purpose, identity and connected systems before production use.
- Grant the smallest set of permissions needed for the current task and define which actions always require approval.
- Collect independent evidence across identity, endpoint, network, cloud and data layers while the agent works.
- Reassess risk continuously and apply a reversible containment action when behavior stops matching the approved purpose.
- Preserve an audit trail, review the outcome and update policy before the next run.
What Guardian Agents and Playbooks are supposed to do
Project Perception already organizes defensive agents into red, blue and green roles. Red agents probe for weaknesses, blue agents investigate and respond to threats, and green agents remediate and harden the environment. The October update adds Guardian Agents that supervise other agents rather than focusing only on conventional attackers.
Playbooks define the desired security outcome, approval boundaries and delegation rules. Guardian Agents can use those playbooks to gather evidence, explain why Dynamic Agent Risk changed, investigate relevant activity and recommend or carry out the allowed containment response. Microsoft says people retain control of objectives and consequential decisions.
That division matters. A Guardian Agent is not a guarantee that another agent will behave correctly, and it should not become an unreviewed super-administrator. The safer design gives the guardian only the authority required for a defined response, logs each decision and reserves high-impact actions for human approval.
Microsoft also emphasizes traceability: security teams should be able to examine what happened, why risk increased and which control acted. That record is essential for incident response, compliance review and tuning. An unexplained autonomous block can interrupt legitimate business just as an unexplained autonomous approval can expose data.
Project Perception and Agent 365 are related, not interchangeable
Microsoft Agent 365 is described as a control plane for observing, governing and securing agents across Microsoft 365 and third-party services. It focuses on inventory, ownership, lifecycle, identity, governance and enterprise administration. Project Perception is the agentic security system that coordinates specialized defenders, playbooks, signals and containment across the cyber stack.
Microsoft says the two products share a unified registry, signals and context. In practical terms, Agent 365 can help IT and security teams agree on which agents exist and who owns them, while Project Perception can use broader security evidence to assess behavior and coordinate a response. Organizations should confirm which controls live in each product, which licenses apply and whether a connector supports the agents they actually run.
What is actually available now
Microsoft Learn currently labels Project Perception as a Limited Public Preview. That means access is restricted to a small, invitation-only group for a defined preview window, and Microsoft warns that prerelease information can change before commercial release. The product page says Perception initially brings coordinated defense into Microsoft Defender and will extend across more Microsoft Security products over time.
The current documentation covers setting up available agents, starting sessions, using chat and playbooks, monitoring work, and approving, rejecting or stopping agentic actions. Individual agents have their own prerequisites and limits. For example, Microsoft’s Recon Agent documentation says it uses read-only API access and that its AI-generated findings must be checked for accuracy.
Microsoft 365 E7 is a commercially listed enterprise subscription at $99 per user per month, paid yearly, before contract-specific pricing. Microsoft positions it above E5 with Agent 365, agent observability and governance, advanced security and compliance, secure access, and productivity applications. That price does not mean every Project Perception workload is included without additional cost.
Microsoft’s Project Perception page states that Perception uses consumption-based, pay-as-you-go pricing, with different task intensities measured at different rates. A buyer should therefore request a written estimate covering licenses, expected agent sessions, log retention, connected services and any separate Security Copilot or Azure consumption before treating the headline E7 price as a complete budget.
What IT teams should verify before deployment
- Preview status: identify which Guardian Agents, playbooks and containment actions are enabled in the tenant today.
- Agent coverage: confirm whether the registry includes Microsoft-built, custom and third-party agents used by the organization.
- Identity boundaries: map every agent to an owner, purpose, credential type, expiration policy and emergency disable path.
- Approval rules: require a person for destructive, financial, external-communication and privilege-changing actions.
- Evidence sources: document which identity, endpoint, network, cloud, application and data signals feed risk decisions.
- Containment scope: test exactly what pause, block, permission reduction or session termination does to active work.
- Auditability: confirm that investigators can reconstruct inputs, actions, approvals, policy changes and final outcomes.
- Costs: model Microsoft 365 E7 seats separately from Project Perception consumption and supporting cloud services.
- Exit plan: preserve logs and define how agents will be disabled or migrated if the preview changes.
A safe pilot plan
Start with one narrow, reversible workflow that uses non-production or low-sensitivity data. Choose an agent whose owner, purpose and success criteria are already clear. Give it read-only access where possible, require approval for every write, and define a small set of behaviors that should trigger a pause.
Run normal and adversarial scenarios. Test stale data, conflicting instructions, prompt injection inside a document, a request for an unnecessary permission and an attempt to contact an unapproved endpoint. Verify that detections are understandable and that containment stops the risky step without destroying unrelated work.
Measure false positives, time to review, evidence quality and operational cost—not only whether the agent finished the task. A system that blocks every unusual action may look secure in a demo but create so much friction that teams disable it. A useful pilot should show that the guardrails improve safety while preserving enough productivity to justify deployment.
Do not let the preview protect the most consequential process on day one. Expand gradually after security, IT, legal, privacy and the business owner agree on acceptable risk, retention and human-approval rules.
What this means for ordinary Microsoft 365 users
Most home and small-business users will not configure Project Perception. The announcement is aimed at organizations running many agents with access to enterprise systems. The consumer takeaway is still relevant: an AI feature that can act across email, files, accounts or purchases deserves narrower permissions and more oversight than a chatbot that only drafts text.
Before connecting any agent, review which accounts it can read, whether it can send or edit, how to revoke access and whether important actions pause for confirmation. Avoid granting broad administrator rights merely to simplify setup. The same principle Microsoft applies at enterprise scale—separate intelligence from authority—works for personal automation too.
A practical Zero Trust reading option
For a grounded introduction to limiting trust and designing around verified access, you can read Project Zero Trust by George Finney on Amazon. The book is not a guide to Project Perception, but its business-focused approach to identity, segmentation and least privilege provides useful background for evaluating agent controls.
As an Amazon Associate, ReaderSpice earns from qualifying purchases.
Bottom line
Microsoft’s October 19 update identifies a real security shift: AI agents do not need malicious intent or an external compromise to become dangerous insiders. Their authority, speed and changing context are enough to justify independent identity controls, continuous evidence and containment that the model cannot override.
Project Perception’s Guardian Agents and Playbooks are Microsoft’s proposed implementation, but buyers should treat them as preview technology. Verify tenant access, product boundaries, approval behavior and total cost before deployment. The durable lesson is broader than one vendor: inventory every agent, grant the least privilege, watch what it actually does and keep a tested human-controlled stop mechanism.
Sources
Microsoft Security Blog: Agents are your newest insiders. Security must move at their speed.
The Official Microsoft Blog: Securing the agentic insider
Microsoft Security: Project Perception overview, agents, availability and pricing
Microsoft Learn: What is Project Perception?
Microsoft Learn: Use the Recon Agent in Project Perception
Microsoft Security: Microsoft 365 enterprise plans and E7 pricing