Microsoft is expanding its Sovereign Cloud portfolio with controls intended for governments, critical infrastructure and regulated organizations that cannot treat every workload like a standard public-cloud application. Announced October 20, 2026, the update spans Azure’s public cloud, customer-operated Azure Local environments and independently operated partner clouds.
The headline is not a new region or a single “sovereign” product. It is a workload-by-workload model: keep appropriate services in the public cloud, place sensitive systems under additional access and key controls, and run essential workloads locally—or disconnected—when continuity and jurisdiction require it. Several capabilities are generally available, but many important items are still previews, limited previews or planned for Microsoft Ignite.
Microsoft Sovereign Cloud update at a glance
- The Sovereign Control Panel enters public preview at Microsoft Ignite.
- Data Guardian adds EU-resident oversight for qualifying Microsoft engineer access in the EU and EFTA.
- Production Touch Ledger creates tamper-evident records of in-scope operational access and actions.
- External key management for Azure Managed HSM is generally available, while its Private Link connection remains preview.
- Connected-to-disconnected transition for Sovereign Private Cloud enters public preview.
- Foundry Local and GitHub Enterprise Local expand locally operated AI and development options.
These items solve different problems. A dashboard improves visibility; it does not create sovereignty by itself. External keys change custody; they do not move application data. Disconnected operation supports continuity; it also introduces hardware, staffing, update and recovery responsibilities.
One continuum, three operating models
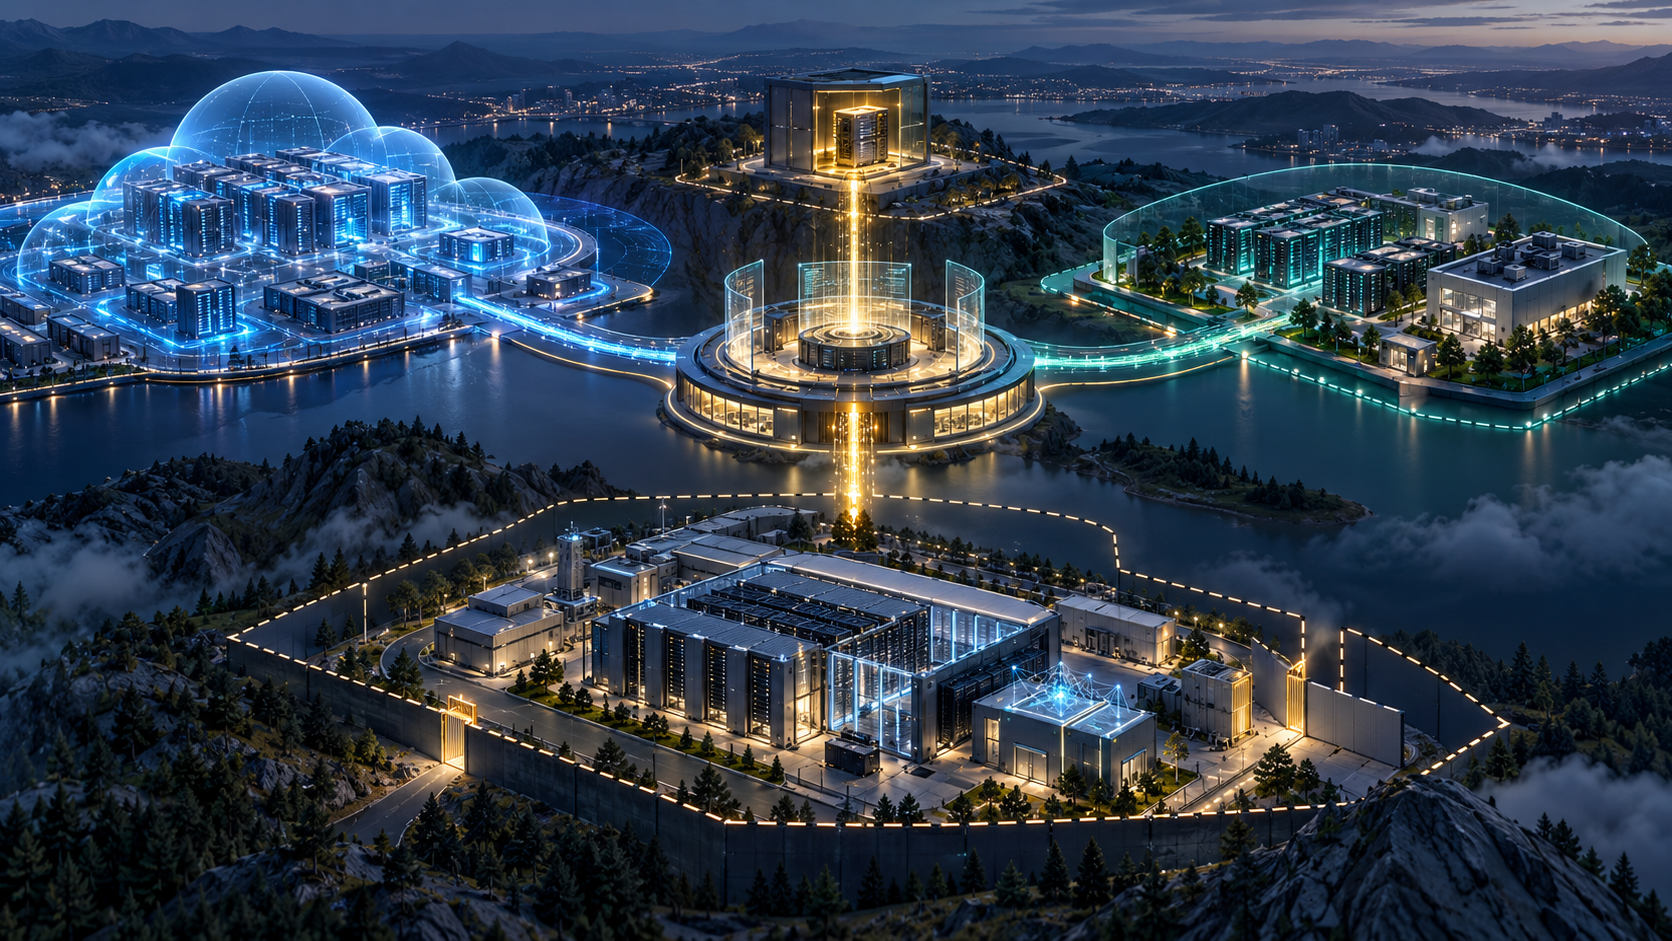
Sovereign Public Cloud
Microsoft’s public-cloud option adds controls around residency, confidentiality, operator access, policy and continuity while retaining Azure’s global service model. It is designed for workloads that can use public-cloud scale but need stronger evidence about who accessed production systems, which controls are configured and where sensitive processing occurs.
Sovereign Private Cloud
Built on Azure Local, the private model runs in infrastructure the customer operates. Microsoft says it can support connected and disconnected environments, local databases, development tools, AI inference and selected productivity services. This is aimed at systems that must keep operating when external connectivity or cloud access is restricted.
Sovereign Partner Ecosystem
The third path uses independently operated and specialized partner environments. Microsoft cites national partner clouds such as Bleu in France and Delos Cloud in Germany, plus local service providers and software partners. The attraction is local operating authority and expertise, but customers still need to understand the exact contract, ownership model, support chain and technical boundary.
What the Sovereign Control Panel does
The new Sovereign Control Panel is scheduled to enter public preview at Microsoft Ignite. Microsoft describes it as a unified Azure portal experience for understanding sovereignty posture, applying controls, finding gaps and assessing workload dependencies and portability.
That can reduce spreadsheet-driven audits, but it should be read as a management layer rather than a compliance certificate. Legal and regulatory obligations vary by country, industry and data type. A green indicator cannot prove that a workload’s business process, supplier chain or human access model satisfies every requirement.
Organizations considering the preview should ask which Azure resources are covered, how often evidence refreshes, whether findings export to existing governance tools and which controls require separate licensing or regional eligibility.
Data Guardian and Production Touch Ledger
For qualifying production systems in the European Union and European Free Trade Association, Data Guardian adds oversight by a trusted EU partner when a Microsoft engineer requests remote access. Customer Lockbox and just-in-time access remain part of the broader operator-access lifecycle.
Production Touch Ledger is intended to record in-scope access and actions in a tamper-evident form. Microsoft says both capabilities are rolling out in phases. That means customers should verify whether their tenant, service, geography and support scenario are included before describing the controls as active.
Neither feature means Microsoft personnel can never touch a system. The goal is controlled, visible and reviewable access. Security teams still need alerting, retention, incident-response ownership and a process for deciding whether a requested support action is justified.
External encryption keys move the root of trust
Azure Key Vault Managed HSM external key management is now generally available. It lets an organization keep the root key-encryption key in hardware it owns and operates on-premises or through a trusted third party. Azure Managed HSM remains the interface and policy layer for supported services, while an external key management proxy translates approved wrap and unwrap operations to the external HSM.
This architecture is significant for organizations whose legal or contractual rules require physical custody outside Microsoft infrastructure. It does not mean bulk application data is encrypted or decrypted inside the external device. Azure services continue to use data-encryption keys; the externally held key protects the key hierarchy.
Microsoft’s documentation also treats external key management as a specialized choice rather than the default. It adds dependency on external HSM availability, proxy design, certificates, latency, recovery procedures and key-operator discipline. Private Link integration for the proxy is still in preview. A lost or unavailable root key can create a serious outage, so key custody must include tested backup and recovery—not merely ownership.
Disconnected operation is not a simple offline switch
Microsoft says the ability to transition selected Sovereign Private Cloud workloads from connected to disconnected operation is entering public preview. Azure Local disconnected operations provide a local control plane for virtual machines, containers and supported Azure Arc-enabled services without a live connection to Azure public cloud.
Running disconnected changes the operating model. The customer must plan extra capacity for the local control plane, transfer signed update packages through a controlled process, monitor certificate lifecycles and maintain local identity, backup and recovery. Some cloud services and integrations are unavailable or behave differently without connectivity.
The feature is most relevant to defense, emergency services, industrial sites, research facilities and essential infrastructure where a network disruption cannot stop operations. Ordinary enterprises should not choose disconnection solely for reassurance; the additional complexity can reduce security if patching, monitoring and staffing are weaker than the connected alternative.
Local data, development and AI expand
Microsoft is bringing more of the application lifecycle into Azure Local. SQL Server is already generally available for connected and disconnected deployments. DocumentDB and Blob Storage are entering public preview, giving customers more local data-service options.
GitHub Enterprise Local is planned for general availability at Ignite as a validated GitHub Enterprise Server appliance on Azure Local. Microsoft also says developers can use GitHub Copilot with locally hosted models for inference, reducing how far code and prompts need to travel. GitHub’s current Azure Local documentation still describes the deployment as public preview, so teams should confirm the final Ignite release status before production.
Foundry Local is also planned for general availability at Ignite for connected and disconnected Azure Local environments. The expanded catalog is expected to include Microsoft, partner, open-weight and open-source models. Local inference and retrieval can answer questions against enterprise data without sending every request to a public endpoint.
Microsoft 365 Local remains a more limited proposition. The current overview centers on customer-operated Exchange Server, SharePoint Server and Skype for Business Server on Azure Local, while the October announcement describes preview access for approved customers and integration with local AI scenarios. It should not be confused with a fully offline copy of every Microsoft 365 cloud service.
Confidential computing and clean rooms
Confidential virtual machines on Azure Local are generally available. They use hardware-encrypted memory and isolation to protect supported data while it is being processed, with attestation before sensitive data or keys are released.
Azure Confidential Clean Rooms are in limited preview. The aim is to let multiple parties analyze approved shared data while reducing exposure of the underlying records. A clean room does not automatically make data anonymous or eliminate contractual duties; participants must still define allowed queries, outputs, retention and re-identification protections.
What IT and compliance teams should verify
- Classify workloads by residency, access, continuity and confidentiality needs before choosing an operating model.
- Separate generally available controls from public preview, limited preview and future Ignite commitments.
- Confirm regional eligibility for Data Guardian, Production Touch Ledger and partner-operated environments.
- Map every external-key dependency, including HSM, proxy, certificates, network path, recovery and operator roles.
- Test disconnected updates, identity, backups and restoration—not only application startup.
- Document which AI models, prompts, retrieval indexes and logs remain local.
- Validate claims with legal, security and operations teams instead of treating the product name as compliance evidence.
Teams building a governance program may find Project Zero Trust by George Finney on Amazon useful background for identity, least privilege and verification principles. It is not Microsoft product documentation and should supplement—not replace—the official architecture, licensing and regulatory review.
As an Amazon Associate, ReaderSpice earns from qualifying purchases.
Who should care about this update
The announcement matters most to public-sector bodies, financial services, healthcare, utilities, telecom providers, defense suppliers and multinationals operating under conflicting data rules. It also gives cloud architects a clearer vocabulary for separating residency, operational access, key custody and continuity instead of compressing all four into the word “sovereignty.”
Smaller organizations may use only a few of these controls. Customer-managed keys, confidential computing, documented operator access and tested business continuity can still be valuable without deploying a disconnected private cloud. The right design is the least complex one that meets the workload’s actual risk and legal requirements.
Bottom line
Microsoft’s October 20 update makes Sovereign Cloud more concrete: a portal for posture, EU-based access oversight, tamper-evident operational records, customer-held root keys and a broader local stack for data, code and AI. It also exposes the tradeoff. Greater control transfers more engineering and operational responsibility to the customer.
The safest reading is precise. External key management is generally available; the Sovereign Control Panel and connected-to-disconnected transition are previews; Confidential Clean Rooms are limited preview; and several Ignite items are planned rather than universally deployed. Treat sovereignty as an architecture and operating practice, then verify every feature against the exact region, service and release stage.
Sources
Official Microsoft Blog: Advancing digital sovereignty with greater control and choice
Microsoft Sovereign Cloud product overview and controls
Microsoft Learn: Managed HSM external key management overview
Microsoft Learn: Azure Local disconnected operations overview
Microsoft Learn: Foundry Local disconnected operations
GitHub Docs: GitHub Enterprise Server on Azure Local
Microsoft Learn: Microsoft 365 Local overview