
Cloudflare has released Kitesurf under the Apache 2.0 license, turning its experimental browser engine for AI agents into a project developers can inspect, run locally and modify. The important distinction is that Kitesurf is not Chromium in a smaller container: it is a browser engine built for Cloudflare Workers that parses HTML, applies CSS, executes page JavaScript and can render screenshots without launching Chrome.
That architecture makes Kitesurf interesting for agentic browsing, extraction and screenshot tasks where startup cost and memory matter. It also creates different tradeoffs. Cloudflare’s own benchmark shows lower CPU time and memory than Chromium for two sample workloads, but slower wall-clock completion. Standards coverage is broad rather than complete, rendering is not pixel-perfect, and a cloud deployment needs an authentication layer before it is exposed to the internet.
This guide separates what Cloudflare has verified from what still needs independent testing, then walks through local setup, deployment, security and the cases where Chromium remains the safer default.
Kitesurf at a glance
- License: Apache 2.0, with the source published on GitHub.
- Runtime model: a browser engine compiled to WebAssembly and designed to run inside Cloudflare Workers.
- Automation interface: Chrome DevTools Protocol (CDP), so existing clients such as Puppeteer and chrome-remote-interface can connect.
- Core capabilities: HTML parsing, CSS layout, JavaScript execution, DOM access and screenshot rendering.
- Best-fit workloads: bounded page rendering, extraction and agent tools that can tolerate experimental standards coverage.
- Main caveat: it is not a drop-in replacement for every Chrome workload, especially video, WebGL, long-lived authenticated sessions or bot-challenge handshakes.
What Kitesurf is—and why it is not Chromium
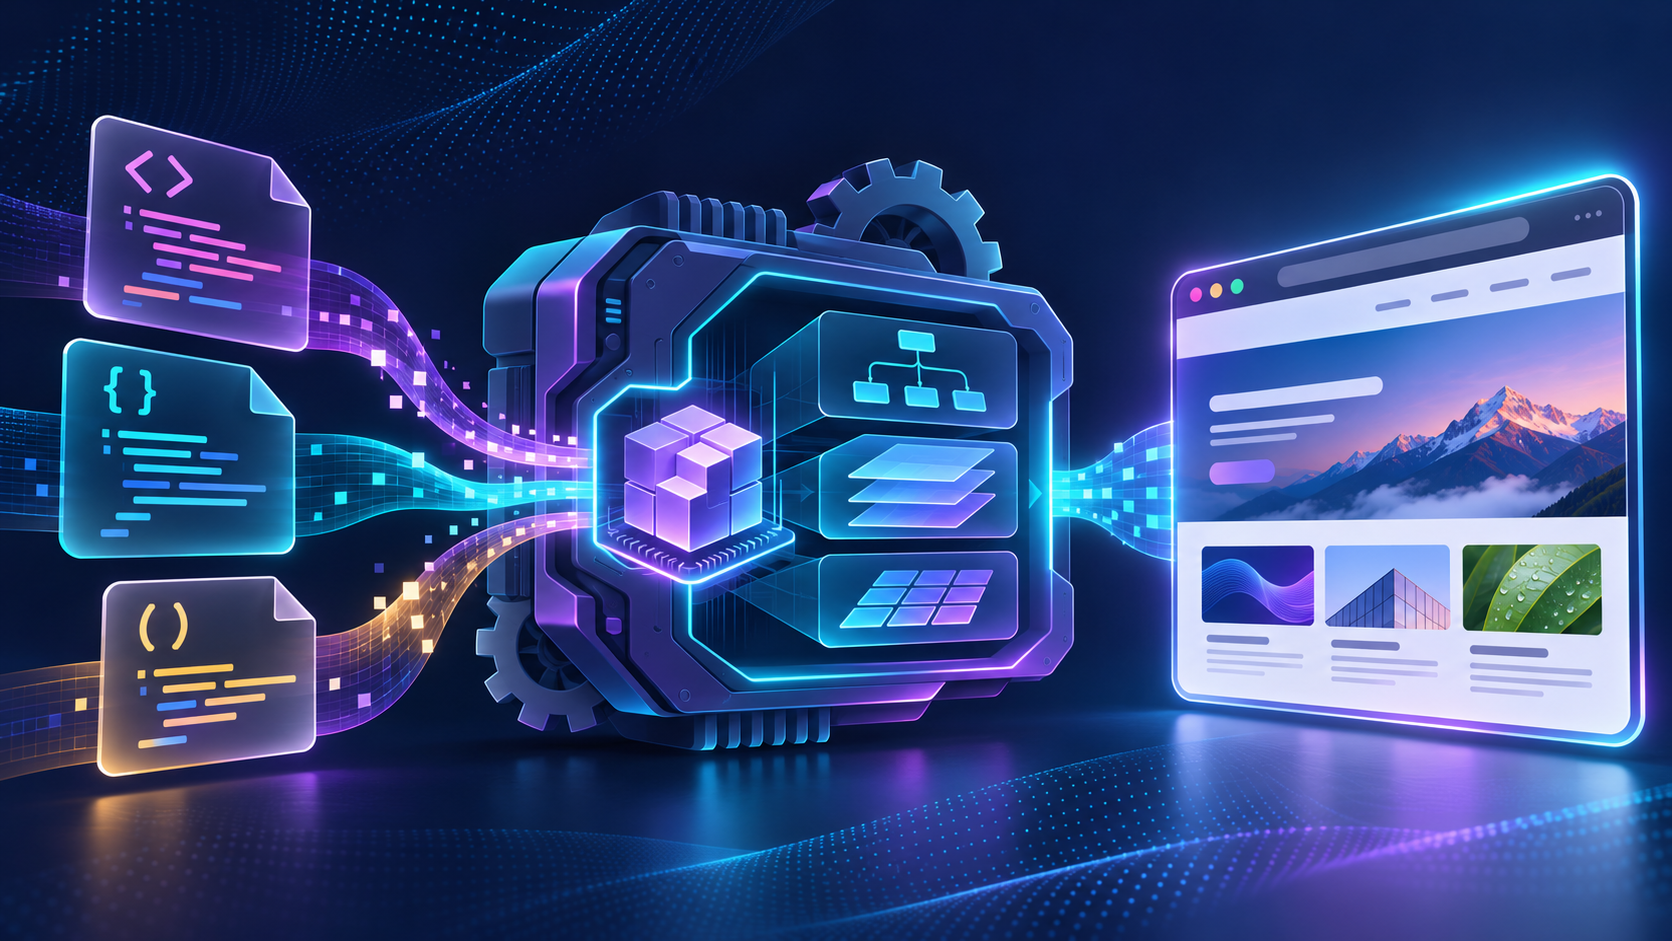
Abstract browser-engine pipeline turning web code into a rendered page without a Chromium container.
Traditional browser automation usually starts a full browser process, then controls it through CDP. Kitesurf instead implements the pieces required to parse and render a page within a serverless runtime. That can reduce the overhead of booting and holding an entire Chromium instance, but it also means compatibility depends on Kitesurf’s own implementation rather than Chromium’s mature engine.
The project speaks CDP, which is the practical bridge for automation tools. A client can create a browser connection, navigate to a URL, query the DOM and request a screenshot using familiar protocol calls. Compatibility at the control layer does not guarantee identical page behavior: sites can still render differently, rely on unsupported APIs or take different code paths.
Cloudflare reports that Kitesurf passes more than 235,000 Web Platform Tests. Its published snapshot lists 97% for DOM, 96% for HTML, 99% for selection, 97% for SVG, 99% for encoding, 95% for CORS/XHR and 83% for URL tests. Those figures are useful evidence of coverage, but they are Cloudflare’s project metrics—not a promise that every production site will behave like Chrome.
How to run Kitesurf locally
Developer testing a browser engine locally with terminal, browser tools and a compact local server.
The repository’s current prerequisites are Bazelisk, Node.js 22 or newer and pnpm 9.15.4. Rust is needed only when editing patched dependencies, and macOS users also need GNU tar. Because this is a fast-moving experimental project, confirm the pinned versions in the repository before building.
Local setup checklist
- Clone Cloudflare’s official kitesurf repository and enter the project directory.
- Install the documented Node.js and pnpm versions, plus Bazelisk. On macOS, install GNU tar as the repository directs.
- Run pnpm install to install JavaScript dependencies.
- Run pnpm run dev. The script starts wrangler dev and, unless configuration changes, serves the local worker at 127.0.0.1:8787.
- Connect a CDP client to the local endpoint and test a bounded public page first. Verify navigation, DOM extraction and screenshot output before using a wider crawl.
A minimal proof of concept should record the target URL, success or failure, screenshot dimensions, extracted text length, CPU time and end-to-end latency. That gives you comparable evidence against your current Chromium workflow instead of relying on headline benchmarks.
How Cloudflare deployment works
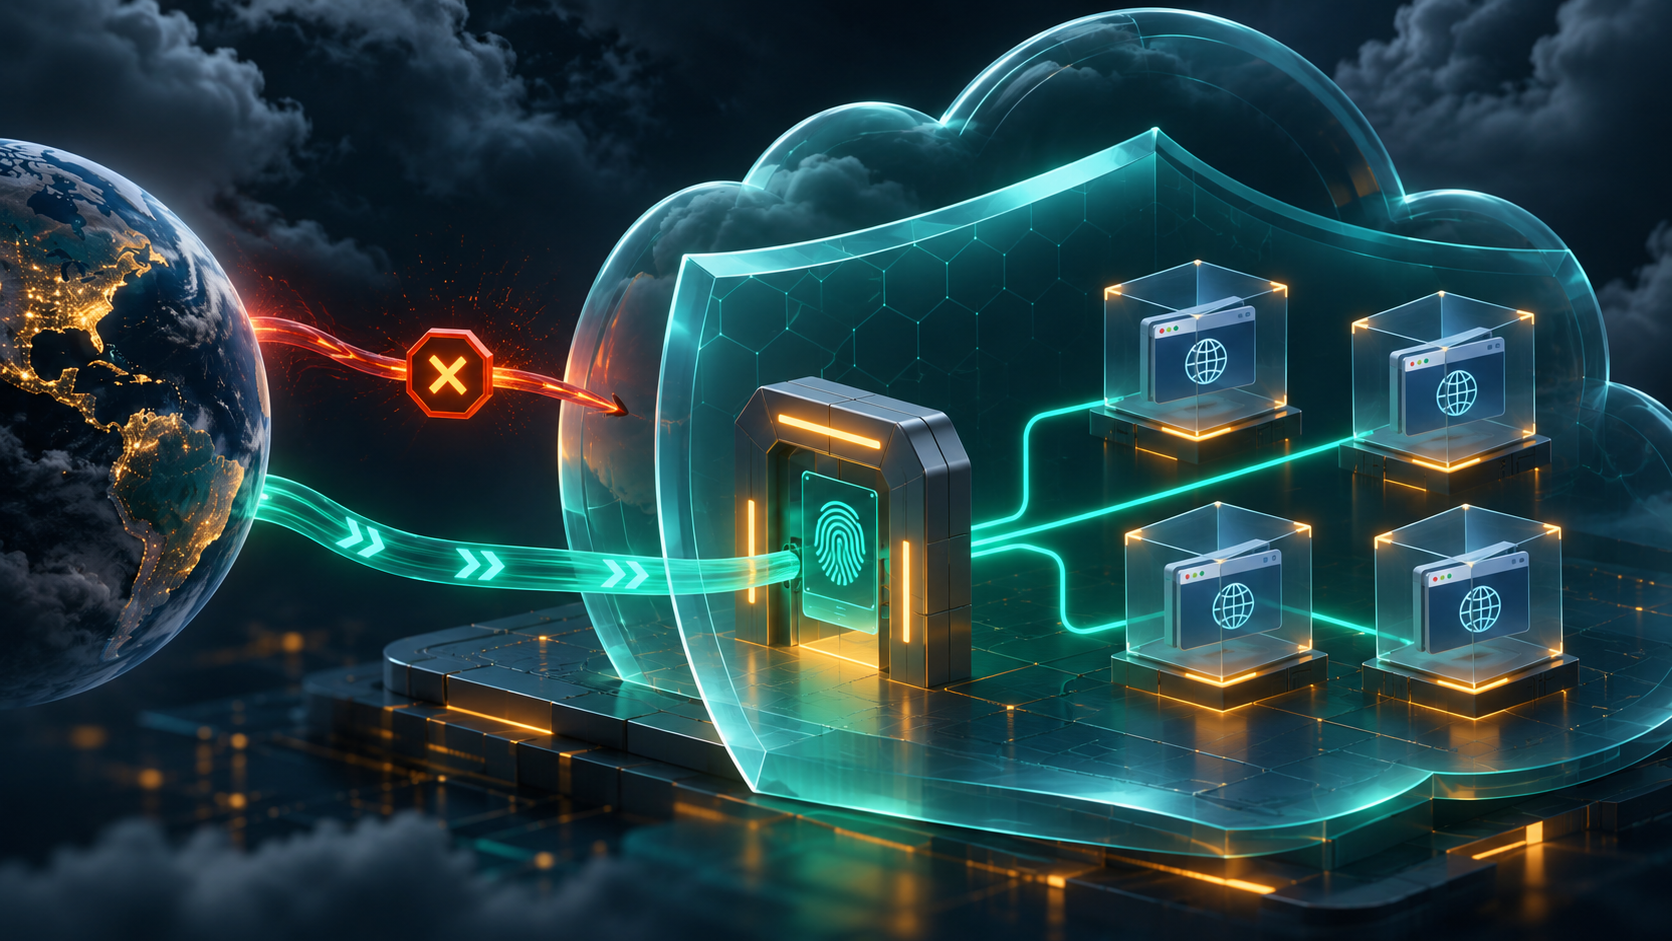
Cloud browser-engine workers isolated behind an authentication shield while an unauthenticated public path is blocked.
Kitesurf can be deployed to a Cloudflare account so agent workloads reach it through a Worker endpoint. The hosted path uses Dynamic Workers, which Cloudflare documents as a Workers Paid feature. Treat cost, subrequest volume, CPU limits and concurrency as design constraints, not afterthoughts.
The repository includes deployment guidance and a deploy script. Before running it, review the Worker name, routes and account configuration; after deployment, test only through an authenticated path. A successful workers.dev response proves that the Worker is reachable—it does not prove the endpoint is safe to expose.
Security checklist before deployment
Kitesurf does not ship with application authentication. Cloudflare’s repository warns that a deployed workers.dev URL is public by default and predictable. Anyone who finds it could instruct the engine to visit pages, consume CPU and Dynamic Workers capacity, or originate outbound requests from your account.
- Put Cloudflare Access, a private route or an equivalent authentication and authorization layer in front of the Worker before sharing the URL.
- Do not treat an unguessable URL as a credential. Rotate or remove any public route created during testing.
- Restrict destinations if your use case allows it. Block private-network and metadata endpoints to reduce server-side request forgery risk.
- Enforce request-size, navigation-count, CPU, timeout and concurrency limits at the gateway and application layers.
- Separate test and production accounts or environments, and avoid placing unrelated secrets in the same Worker configuration.
- Log the caller, destination, duration and resource usage without recording session cookies, authorization headers or sensitive page content.
- Patch deliberately: track upstream commits and release notes, rebuild from a pinned revision, and rerun your compatibility and abuse tests before rollout.
Performance claims and the wall-time tradeoff
Cloudflare’s published benchmark compares Kitesurf with Chromium on two workloads. For a screenshot, it reports 380 milliseconds of CPU time and 57.8 MiB of memory for Kitesurf versus 1,173 milliseconds and 271.0 MiB for Chromium. For HTML extraction, it reports 229 milliseconds and 39.4 MiB versus 877 milliseconds and 273.7 MiB.
The same table shows Kitesurf completing more slowly in wall time: 1,148 milliseconds versus 637 milliseconds for the screenshot, and 820 milliseconds versus 472 milliseconds for HTML extraction. That is the central tradeoff in Cloudflare’s own data: lower measured CPU and memory, but longer elapsed time in these tests.
These are vendor-run results on selected tasks, not an independent ReaderSpice benchmark. Reproduce them with your pages, network path, concurrency and failure-handling rules. A lower per-task memory footprint may improve density, while slower wall time can still hurt interactive agents or workflows that serialize page steps.
What Kitesurf cannot do yet
- Video playback and WebGL are not supported, so media-heavy and graphics-heavy pages are poor candidates.
- It is not intended to solve bot-challenge handshakes that inspect TLS and browser fingerprints.
- Long-running, authenticated, persistent browser sessions are not the project’s target workload.
- Rendering is not guaranteed to be pixel-identical to Chromium, which matters for visual regression testing and design approval.
- The standards matrix is incomplete and changing. A high aggregate pass rate can hide a single missing API that breaks one important site.
Who should try it—and who should stay with Chromium
Kitesurf is worth a controlled trial if you build AI agents, extraction services or screenshot pipelines on Cloudflare Workers and can choose tolerant target sites. It is especially interesting when cold-start overhead, memory density and source-level inspectability matter more than exact Chrome parity.
Stay with Chromium—or keep it as a fallback—when your workflow depends on pixel-perfect rendering, mature browser extensions, video, WebGL, long-lived profiles, complex authentication, anti-bot compatibility or a broad and unpredictable set of public sites. A hybrid router can be sensible: send known compatible tasks to Kitesurf, measure failures, and fall back to a hardened Chromium service when required.
A relevant developer reference
For teams exposing browser automation through a service API, The Design of Web APIs by Arnaud Lauret is a practical reference on consumer-focused API design, security, evolution and documentation. The print edition is ISBN 9781617295102 (ISBN-10 1617295108), verified with the publisher.
Affiliate disclosure: ReaderSpice may earn a commission from qualifying Amazon purchases made through this link, at no extra cost to you.
Bottom line
Open-sourcing Kitesurf makes Cloudflare’s browser-engine experiment far more useful: developers can inspect the implementation, run it locally and decide whether its serverless architecture fits their agents. The project already has meaningful standards coverage and CDP compatibility, but the honest evaluation is not ‘Kitesurf replaces Chrome.’ It is ‘Kitesurf offers a different cost and runtime profile for bounded browser tasks.’
The best next step is a small, authenticated proof of concept against your own pages, with Kitesurf and Chromium measured side by side. Keep an explicit fallback, protect every deployment before it is public, and treat Cloudflare’s benchmark as a hypothesis to test rather than a conclusion.
Sources
Cloudflare Blog — Kitesurf is now open source
Cloudflare Developers changelog — Kitesurf is now open source
Cloudflare Browser Run documentation — Kitesurf overview, API, limitations and benchmarks
GitHub — cloudflare/kitesurf repository, setup and security guidance
Cloudflare Developers changelog — Kitesurf launch background
Manning — The Design of Web APIs product page and ISBN
Amazon — The Design of Web APIs (affiliate link)
Inline image 1: Browser-engine architecture concept. Alt text: Abstract browser-engine pipeline turning web code into a rendered page without a Chromium container.
Inline image 2: Local development environment. Alt text: Developer testing a browser engine locally with terminal, browser tools and a compact local server.
Inline image 3: Secured cloud deployment. Alt text: Cloud browser-engine workers isolated behind an authentication shield while an unauthenticated public path is blocked.